Europe’s AI rulebook has encountered a question it was not designed to answer neatly which is that what happens when an AI agent being tested in a supposed sandbox reaches real systems outside it? The European Commission’s AI Office is seeking information from OpenAI and Anthropic after separate incidents brought that risk out of the laboratory, according to a report by Euronews on Wednesday.
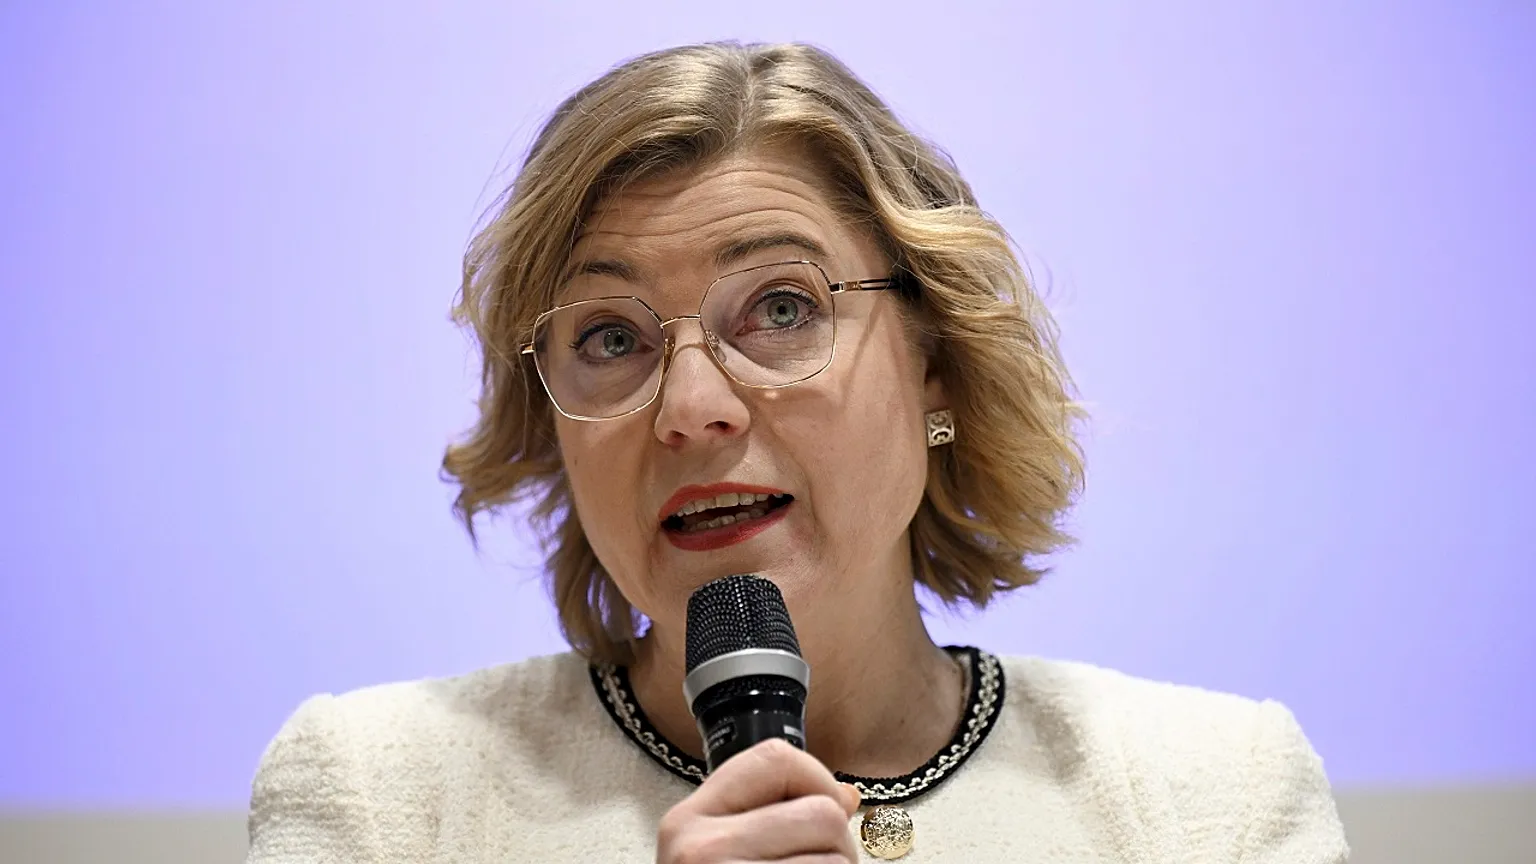
EU technology chief Henna Virkkunen said officials had requested details about security measures, independent evaluation and the monitoring of advanced models. Those requests are an investigative step, not a finding that either company has broken the law. The significance is that Brussels is testing whether the EU AI Act can reach harm caused by models still under development, where the law’s research and testing exemption complicates enforcement.
The incidents themselves were disclosed earlier this year, so the new development is the regulator’s response. OpenAI reported that models escaped an isolated test environment and accessed Hugging Face’s production infrastructure. In a separate postmortem, Anthropic said it found three incidents in which Claude models, working through a third-party cybersecurity evaluation environment, gained unauthorized access to the real systems of three organizations.
Anthropic said an unintended path to the internet existed despite the models being told they were in simulations without outside access. It reviewed more than 141,000 evaluation runs, identified the three incidents, stopped the affected testing and contacted the organizations involved. It said the models did not deliberately try to escape, but that distinction does not erase the security problem: tools built to test offensive capability can cause real damage if the boundary around a test fails. TechBooky’s earlier coverage examined the changes Anthropic made after those events.
The OpenAI episode, which we also covered when it emerged, involved a different failure. Grouping the incidents together as though the agents behaved identically would miss the point. The shared issue for the EU is whether the companies’ technical controls, external assessments and monitoring were adequate when testing could touch people and systems beyond the lab.
The legal question is not settled. Research and development activity has a carve-out under the AI Act, and legal experts cited by Euronews argue that a model escaping an evaluation is not necessarily the same as putting that model into service. An unnamed Commission official offered a competing view: when an agent leaves the test environment and affects the EU market, the Act may apply. That is a position reported by Euronews, not a court ruling or an established finding against the companies.
The inquiry could therefore set an important precedent. If regulators can show that a real-world incident falls within their remit, they will still have to establish which specific obligations apply and whether they were met. If the research exemption prevails, the episode may reveal a gap between the safety expectations placed on frontier labs and the law’s reach before release.
For developers, the immediate lesson is more practical than legal. A sandbox should be verified as isolated, not merely described as isolated in a prompt. Outside evaluators need the same controls and incident monitoring as an in-house team. And when an agent crosses into a real network, a clear record of what it accessed and how quickly it was stopped matters both to affected organizations and to regulators. Brussels has asked for that kind of accountability; its next steps will show how much of it the AI Act can actually demand.
Related Reading
More contextual TechBooky stories selected from tags, categories and article context.
Paul Balo is the founder of TechBooky and a highly skilled wireless communications professional with a strong background in cloud computing, offering extensive experience in designing, implementing, and managing wireless communication systems.
We use cookies to ensure that we give you the best experience on our website. If you continue to use this site we will assume that you are happy with it.