TechBooky AI Assistant
👋 Welcome to TechBooky AI Assistant

I can help with:
🔎 Tech News
🤖 AI Topics
💻 Gadgets
☁️ Cloud
✍️ Guest Posts
📢 Advertising
🔗 Backlinks
📩 Newsletter
  • AI Search
  • Cryptocurrency
  • Earnings
  • Enterprise
  • About TechBooky
  • Submit Article
  • Advertise With TechBooky
  • Contact Us
TechBooky
  • African
  • AI
  • Metaverse
  • Gadgets
Generic selectors
Exact matches only
Search in title
Search in content
Post Type Selectors
Search in posts
Search in pages
  • African
  • AI
  • Metaverse
  • Gadgets
Generic selectors
Exact matches only
Search in title
Search in content
Post Type Selectors
Search in posts
Search in pages
TechBooky
Generic selectors
Exact matches only
Search in title
Search in content
Post Type Selectors
Search in posts
Search in pages
Home Networking

Microsoft To Turn Off NTLM By Default In Future Windows

Akinola Ajibola by Akinola Ajibola
February 1, 2026
in Networking
Share on FacebookShare on Twitter
Share this story

Send it to someone who should read it.

f Facebook X X in LinkedIn wa WhatsApp tg Telegram @ Email
Image Source: Cyber Security News
In Brief
  • In order to prioritise more secure Kerberos-based authentication and due to security flaws that leave businesses vulnerable to cyberattacks, Microsoft said that it will disable the...
  • This modification, which is a component of the “secure-by-default” strategy, attempts to shield enterprises against persistent weaknesses like relay assaults and pass-the-hash exploits.
  • The challenge-response authentication protocol known as NTLM (short for New Technology LAN Manager) replaced the LAN Manager (LM) protocol and was first released with Windows NT...

In order to prioritise more secure Kerberos-based authentication and due to security flaws that leave businesses vulnerable to cyberattacks, Microsoft said that it will disable the 30-year-old NTLM (NT LAN Manager) authentication system by default in future Windows editions. This modification, which is a component of the “secure-by-default” strategy, attempts to shield enterprises against persistent weaknesses like relay assaults and pass-the-hash exploits.

The challenge-response authentication protocol known as NTLM (short for New Technology LAN Manager) replaced the LAN Manager (LM) protocol and was first released with Windows NT 3.1 in 1993.

The default protocol for domain-connected devices running Windows 2000 or later is now Kerberos, replacing NTLM. Even though NTLM employs poor cryptography and is susceptible to assaults, it is nevertheless utilised today as a backup authentication method when Kerberos is unavailable, despite being the default protocol in earlier Windows editions.

Since its introduction, NTLM has been extensively exploited in NTLM relay attacks, where attackers compel compromised network devices to authenticate with attacker-controlled servers, allowing them to escalate privileges and gain full control of the Windows domain. Because NTLM is still in use on Windows servers, attackers can circumvent NTLM relay attack mitigations by taking advantage of vulnerabilities like PetitPotam, ShadowCoerce, DFSCoerce, and RemotePotato0.

Pass-the-hash attacks, in which hackers use malicious software or system flaws to obtain NTLM hashes (hashed passwords) from targeted systems, have also been directed towards NTLM. By using these hashed passwords to authenticate as the compromised user, the attackers are able to steal confidential information and propagate laterally throughout the network.

Microsoft announced on Thursday that NTLM will finally be disabled by default in the upcoming major Windows Server release and related Windows client versions as part of a larger push toward passwordless, phishing-resistant authentication methods. This represents a significant shift away from the legacy protocol and toward more secure Kerberos-based authentication.

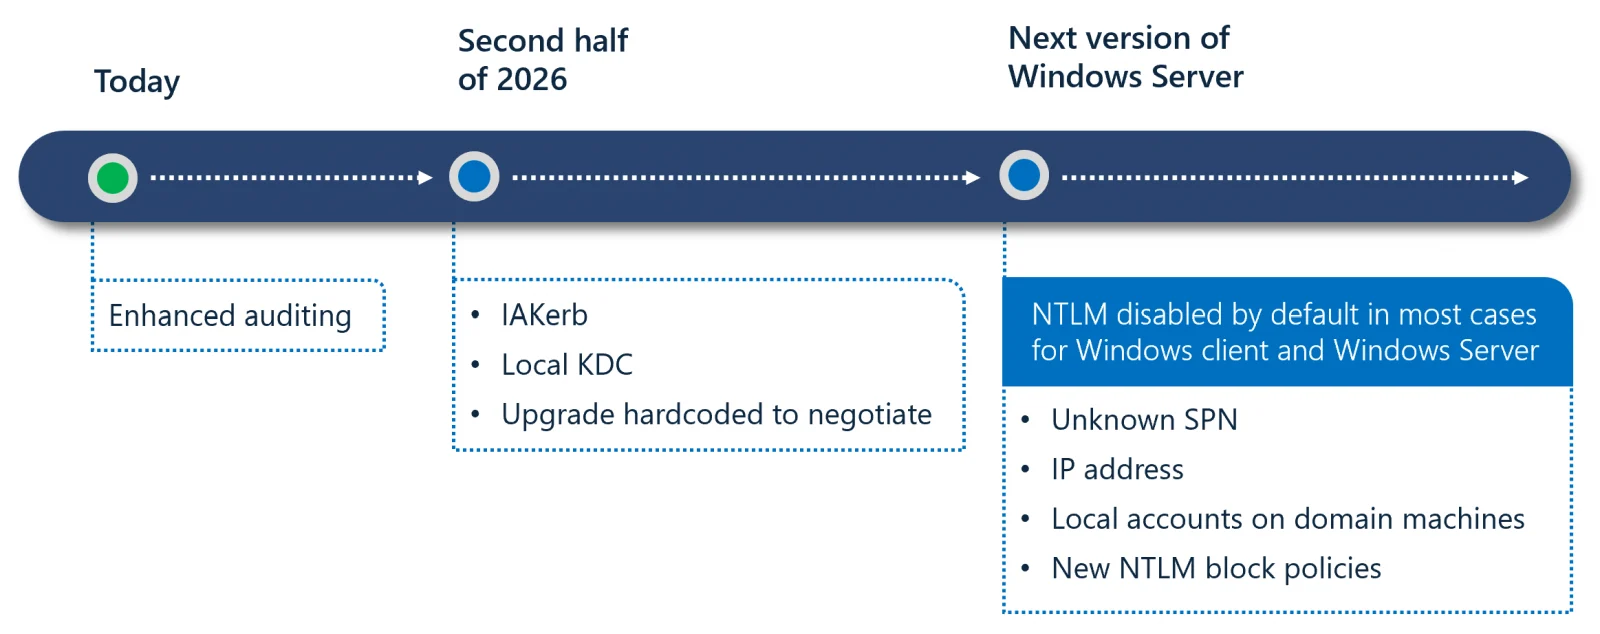
Additionally, Microsoft presented a three-phase transition strategy intended to minimise inconvenience and reduce risks associated with NTLM. In phase one, administrators will be able to determine where NTLM is still in use by using the improved auditing tools found in Windows 11 24H2 and Windows Server 2025.

In order to address typical instances that cause NTLM fallback, phase two, which is slated for the second half of 2026, will provide new features like IAKerb and a Local Key Distribution Center.

Although the protocol will still exist in the operating system and can be specifically re-enabled through policy controls if necessary, phase three will disable network NTLM by default in subsequent releases.

Also worth reading
Microsoft’s Patch Tuesday Shows AI Is Finding Bugs Fast Microsoft And ILO Take Digital Skills Training To Kenya’s Refugee Youth Microsoft’s AI Buildout Runs Into The Hard Math Of Chips And Power Nvidia-Powered Windows PCs Debut as Microsoft Bets on Local AI Computing US Backs OpenAI In Copyright Fight OpenAI And Big Tech Warn The World Has Months To Prepare For AI Hacks

Microsoft said that disabling NTLM by default does not imply that NTLM has yet to be fully removed from Windows. Rather, it means that Windows will be supplied in a secure-by-default state, meaning that network NTLM authentication will no longer be employed automatically.

Modern, safer Kerberos-based alternatives will be preferred by the OS. At the same time, new forthcoming features like Local KDC and IAKerb (pre-release) will solve frequent legacy circumstances.

In October 2023, Microsoft initially declared its intention to retire the NTLM authentication mechanism. It also stated that it wished to provide management controls so that administrators would have more freedom to monitor and limit NTLM usage in their environments.

In July 2024, it also formally deprecated NTLM authentication for Windows and Windows servers, encouraging developers to switch to Kerberos or Negotiation authentication to avoid further problems.

Since 2010, Microsoft has been cautioning developers not to use NTLM in their applications and encouraging Windows administrators to either disable NTLM or set up their servers to use Active Directory Certificate Services (AD CS) to prevent NTLM relay attacks.

To identify programs that still depend on NTLM, configure the environment using the audit user and enable enhanced NTLM auditing, now available in Windows Server 2025.

Mapping dependencies helps determine which hardware or legacy applications, such as older NAS devices, may rely solely on NTLM. Developers should replace NTLM-specific calls with the negotiating protocol, which prioritises Kerberos while retaining a fallback option if needed.

Begin testing “NTLM-off” configurations in non-production environments to detect any potential issues early.

Related Reading

More contextual TechBooky stories selected from tags, categories and article context.

  • Windows_11_25H2
    Microsoft To Remove WMIC After Windows 11 25H2 Upgrade
  • c4398f2d-a521-487b-b68e-c986db06f158
    Microsoft Disables ActiveX in Office 2024 &…
  • Windows_11
    Microsoft Fixes Windows Certificate Enrolment Bug
  • windows-11-surpasses-one-billion-users-despite-mix
    Windows 11 Surpasses One Billion Users Despite Mixed…
  • win10-new-1152x648
    Microsoft’s $1.50 Windows Update Fee Kicks In July 1
  • Microsoft-is-removing-SMS-code-authentication
    Microsoft Drops SMS Codes for Passkey Sign-Ins
  • Screenshot 2023-01-30 at 14.03.31
    Microsoft to Discontinue Remote Desktop Service
  • get-latest-updates-toggle
    Ads Could Be Coming To Windows 11 Shortly
Keep Reading Smarter

Search TechBooky with AI

Use TechBooky's AI Search to explore the context behind this story and related coverage across the site.

Try AI Search
More On This Topic
Networking
Follow TechBooky

Follow TechBooky for more technology stories and newsroom updates.

f Facebook X X in LinkedIn ig Instagram wa WhatsApp

Tags: microsoftnetworkingNT LAN ManagerNTLM
Akinola Ajibola

Akinola Ajibola

Search TechBooky
Open TechBooky AI Search Try the AI Assistant

BROWSE BY CATEGORIES

Receive top tech news directly in your inbox

subscription from
Loading

Freshly Squeezed

  • Amazon Brings Alexa+ To India With Hindi Support September 16, 2026
  • SpaceX Sets September 22 For First Starship Orbital Try September 16, 2026
  • Meta Puts AI Agents Inside WhatsApp Business Setup September 16, 2026
  • US AI Data Centres Could Burn More Gas Than Major Economies September 16, 2026
  • Nvidia Says AI Safety Should Be Left To Builders September 16, 2026
  • Anthropic Takes Claude Into Wealth Management September 16, 2026
  • OpenAI Backs Outside Evaluators For Frontier AI Models September 16, 2026
  • Zuckerberg Says AI Labs Can Slow Down Without A Pact September 16, 2026
  • Google Launches Gemini 3.8 Live For Real-Time AI Talk September 16, 2026
  • Elon Musk Wants AI Rivals To Test Each Other’s Models September 16, 2026
  • Nuance Labs Raises $50M To Make AI Avatars Less Awkward September 15, 2026
  • AI Startup Funding Is Splitting Into Winners And Strugglers September 15, 2026

Browse Archives

September 2026
M T W T F S S
 123456
78910111213
14151617181920
21222324252627
282930  
« Aug    

Quick Links

  • About TechBooky
  • Advertise With TechBooky
  • Contact us
  • Submit Article
  • Privacy Policy
Generic selectors
Exact matches only
Search in title
Search in content
Post Type Selectors
Search in posts
Search in pages
  • African
  • Artificial Intelligence
  • Gadgets
  • Metaverse
  • Tips
  • AI Search
  • About TechBooky
  • Advertise With TechBooky
  • Submit Article
  • Contact us

© 2025 Designed By TechBooky Elite

Discover more from TechBooky

Subscribe now to keep reading and get access to the full archive.

Continue reading

We use cookies to ensure that we give you the best experience on our website. If you continue to use this site we will assume that you are happy with it.