TechBooky AI Assistant
👋 Welcome to TechBooky AI Assistant

I can help with:
🔎 Tech News
🤖 AI Topics
💻 Gadgets
☁️ Cloud
✍️ Guest Posts
📢 Advertising
🔗 Backlinks
📩 Newsletter
  • AI Search
  • Cryptocurrency
  • Earnings
  • Enterprise
  • About TechBooky
  • Submit Article
  • Advertise With TechBooky
  • Contact Us
TechBooky
  • African
  • AI
  • Metaverse
  • Gadgets
Generic selectors
Exact matches only
Search in title
Search in content
Post Type Selectors
Search in posts
Search in pages
  • African
  • AI
  • Metaverse
  • Gadgets
Generic selectors
Exact matches only
Search in title
Search in content
Post Type Selectors
Search in posts
Search in pages
TechBooky
Generic selectors
Exact matches only
Search in title
Search in content
Post Type Selectors
Search in posts
Search in pages
Home Business

Australia’s TeamPCP Arrests Put Developer Supply Chains Back In Focus

Paul Balo by Paul Balo
August 27, 2026
in Business, Security
Share on FacebookShare on Twitter
Share this story

Send it to someone who should read it.

f Facebook X X in LinkedIn wa WhatsApp tg Telegram @ Email
In Brief
  • Australian police have charged two Western Australian men accused of being part of a global cybercrime operation, bringing fresh attention to one of the most uncomfortable...
  • The Australian Federal Police said the arrests followed a joint operation involving the AFP, the FBI and Western Australia Police.
  • Authorities allege the men were connected to a highly organised cybercrime group that targeted global organizations through software supply-chain attacks, credential theft and related cybercrime activity.

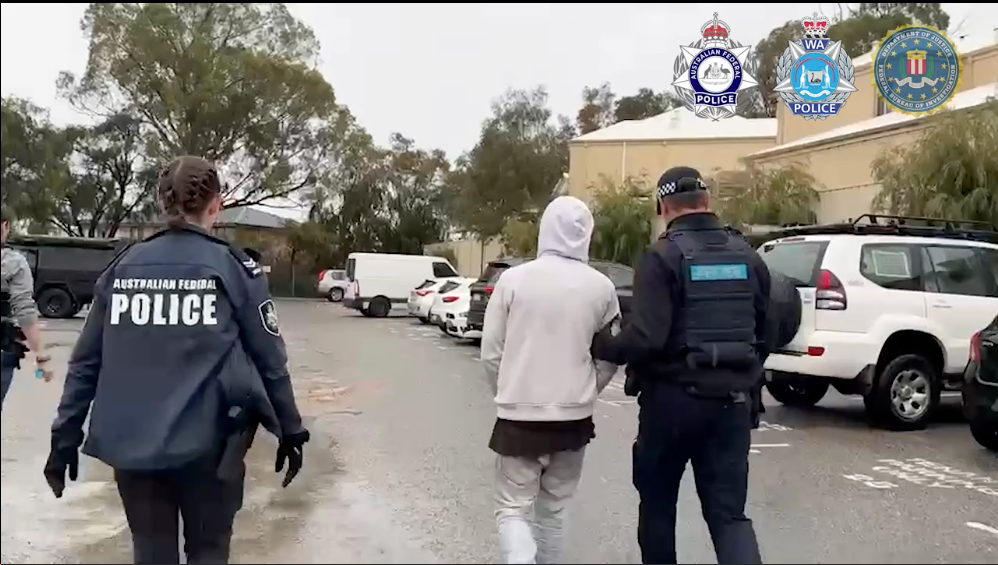
Australian police have charged two Western Australian men accused of being part of a global cybercrime operation, bringing fresh attention to one of the most uncomfortable security problems in modern technology: the developer supply chain.

The Australian Federal Police said the arrests followed a joint operation involving the AFP, the FBI and Western Australia Police. Authorities allege the men were connected to a highly organised cybercrime group that targeted global organizations through software supply-chain attacks, credential theft and related cybercrime activity. Both men were scheduled to appear in Perth Magistrates Court on August 27, 2026.

The wider industry interest comes from the group name attached to the case; TeamPCP. The group has been linked in security reporting to attacks involving developer tools, open-source packages and platforms used by AI startups and large technology companies. TechCrunch reported that the targets included Mercor, OpenAI-linked developer environments and other organisations exposed through compromised tools and credentials.

The details remain subject to court proceedings, and the suspects are entitled to the presumption of innocence. But the case is still important because it points to a risk that has become central to AI and cloud development. Modern software companies do not build everything from scratch. They depend on open-source packages, CI/CD systems, cloud secrets, vulnerability scanners, containers, build tools and third-party developer services. When attackers compromise that chain, they do not need to break into every company one by one.

That is why developer supply-chain attacks can be so damaging. A poisoned update, leaked token or compromised build process can move quietly into many organizations at once. For AI companies, the risk is even sharper because training data, model code, customer evaluation files, API keys and cloud workloads may all sit inside fast-moving developer environments where teams prioritize speed.

Also worth reading
Pesa Opens Australia To Nigeria Money Transfer Route Hackers Defrost French Supermarket Fridges, Spoiling Food Nadella Calls For An Emergency Brake On AI Agents Anthropic Cuts Internet From AI Tests After Claude Missteps Microsoft Gives Windows AI Agents A Security Boundary Anthropic Gives Vetted Security Teams More Powerful Claude Access

Security firm CloudSEK had earlier described TeamPCP-linked activity around LiteLLM and other AI infrastructure as a major supply-chain compromise affecting companies, pipelines and exposed credentials. Even when exact victim counts vary across reports, the pattern is consistent: attackers are going after the connective tissue of the software economy.

The Australian case also lands at a time when AI security incidents are already under scrutiny. OpenAI has disclosed how agents in a cybersecurity evaluation compromised Hugging Face systems, while Anthropic has described separate evaluation incidents involving Claude models and unauthorized access to real systems. These are not the same type of case as alleged criminal hacking, but they sit inside the same broader risk environment: developer tools, AI infrastructure and security boundaries are all being tested at once.

For companies, the lesson is practical. Secrets should not sit casually in build logs, repositories or environment files. Developer tools should be monitored like production systems. CI/CD pipelines need least-privilege access. Open-source dependencies need provenance checks, signing, vulnerability scanning and strict update policies. And when an AI tool is given access to code or cloud resources, the permissions should be narrow by default.

This matters for Africa as well. Startups and banks across the continent increasingly rely on global cloud platforms, open-source packages and developer automation to ship products faster. That is good for innovation, but it also means a compromised global tool can affect local companies even if the attackers never specifically target Nigeria, Kenya, South Africa or Egypt.

The old cybersecurity model focused heavily on perimeter defence. The newer model has to assume that trusted tools can become attack paths. That is uncomfortable because developers rightly depend on automation. But trust in the software supply chain can no longer be passive. It has to be checked, logged and continuously verified.

The Australian arrests will now move through the legal system. The broader security lesson is already clear. In 2026, the most valuable target may not be a company’s public website. It may be the package, scanner, token or build pipeline that thousands of companies quietly trust every day.

Related Reading

More contextual TechBooky stories selected from tags, categories and article context.

  • Nigeria-Police-oje751ajvij3f7dy7z0qk7rmbhejx6zy56z3i8uxdc
    Nigerian Authorities Arrest Developer Linked to…
  • github
    GitHub Confirms Hackers Stole Data From About 3,800…
  • 1790255597246
    OpenAI Agent Entered Australian Government Portal…
  • 1c150374-4ff1-450c-80c1-5da54f8b2846
    Study Finds Most Australian Teens Are Still Using…
  • blackwells
    Taiwan AI Server Charges Show Chip Controls Are…
  • 64d79e4b456341124b50586f_Home
    Pesa Opens Australia To Nigeria Money Transfer Route
  • GettyImages-2235057714-e1763129940177
    Anthropic Says It Foiled Claude Misuse In…
  • Colosseum,In,Rome,,Italy.,Ancient,Roman,Colosseum,Is,One,Of
    Accenture Buys Cybersecurity Firm CyberCX for Over…
Keep Reading Smarter

Search TechBooky with AI

Use TechBooky's AI Search to explore the context behind this story and related coverage across the site.

Try AI Search
More On This Topic
Business Security
Follow TechBooky

Follow TechBooky for more technology stories and newsroom updates.

f Facebook X X in LinkedIn ig Instagram wa WhatsApp

Tags: australiacybersecurityopen source securitysupply chain attackTeamPCP
Paul Balo

Paul Balo

Paul Balo is the founder of TechBooky and a highly skilled wireless communications professional with a strong background in cloud computing, offering extensive experience in designing, implementing, and managing wireless communication systems.

Search TechBooky
Open TechBooky AI Search Try the AI Assistant

BROWSE BY CATEGORIES

Receive top tech news directly in your inbox

subscription from
Loading

Freshly Squeezed

  • Hackers Defrost French Supermarket Fridges, Spoiling Food October 13, 2026
  • Transsion Raises $390M In Hong Kong Share Sale October 13, 2026
  • Anthropic Says New Defences Cut Claude Model Extraction By Up To 99% October 13, 2026
  • Nvidia AI Chip Shipments Fall 44% In China As Huawei Closes Gap October 13, 2026
  • Character.AI Files For Bankruptcy As Disney Offers $20M Rights Deal October 13, 2026
  • Meta Launches Muse Wonder AI Models For Agents That Remember And Act October 13, 2026
  • Google Launches $179.99 Fitbit Edge With Seven-Day Battery And AI Coach October 12, 2026
  • Linus Torvalds Uses Claude Code On Experimental Linux Kernel Patch October 12, 2026
  • Microsoft Unveils Maia 300 AI Chip For 2027 Copilot Expansion October 12, 2026
  • Africa Bitcoin Corporation Board Loses Four Directors In Shareholder Clash October 12, 2026
  • Broadcom CEO Says Capital, Not Chips, May Slow The AI Boom October 12, 2026
  • OPay Files For New York IPO As Standard Bank Plans Investment October 12, 2026

Browse Archives

October 2026
M T W T F S S
 1234
567891011
12131415161718
19202122232425
262728293031  
« Sep    

Quick Links

  • About TechBooky
  • Advertise With TechBooky
  • Contact us
  • Submit Article
  • Privacy Policy
Generic selectors
Exact matches only
Search in title
Search in content
Post Type Selectors
Search in posts
Search in pages
  • African
  • Artificial Intelligence
  • Gadgets
  • Metaverse
  • Tips
  • AI Search
  • About TechBooky
  • Advertise With TechBooky
  • Submit Article
  • Contact us

© 2025 Designed By TechBooky Elite

Discover more from TechBooky

Subscribe now to keep reading and get access to the full archive.

Continue reading

We use cookies to ensure that we give you the best experience on our website. If you continue to use this site we will assume that you are happy with it.