DevOps teams have been advised by security researchers to fix a high-severity vulnerability in Grafana, a widely used tool, that may be exposing them to account takeover attempts as over 46,000 Grafana instances that are visible to the internet are still unpatched and vulnerable to a client-side open redirect vulnerability that permits the execution of a malicious plugin and account takeover.
Multiple iterations of the open-source platform used to monitor and visualize infrastructure and application metrics are affected by the vulnerability, which is recorded as CVE-2025-4123.
Bug bounty hunter Alvaro Balada found the vulnerability, which Grafana Labs fixed in security upgrades published on May 21.
According to researchers from application security firm OX Security, who call the problem “The Grafana Ghost,” as of this writing, approximately one-third of all Grafana instances accessible over the public internet had not been fixed.
The goal of the analysts’ effort, they told BleepingComputer, was to show that Balada’s discovery could be weaponized.
They evaluated the exposure by comparing the data with the platform’s spread throughout the ecosystem after identifying the versions that were susceptible to the assault.
Of the 128,864 instances they discovered online, 46,506 were still running exploitable versions. This amounts to roughly 36% of the total Grafana instances that are visible to the public, in addition to innumerable Grafana servers that are not online. This was announced on Sunday by Ox Security and issued a warning about CVE-2025-4123.
DevOps engineers, sysadmins, and developers utilize Grafana, an open source analytics and visualization tool, to keep an eye on infrastructure and system performance.
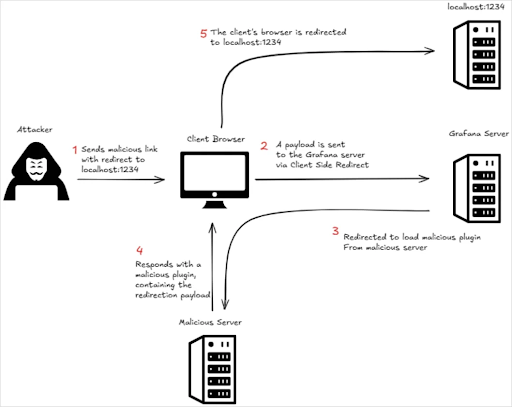
Through a series of exploitation steps that combine client-side path traversal with open redirect mechanics, OX Security’s thorough analysis of CVE-2025-4123 revealed that attackers can trick victims into clicking URLs that cause a malicious Grafana plugin to load from a site under the threat actor’s control.
The National Vulnerability Database (NVD) describes it as a cross-site scripting (XSS) vulnerability brought on by combining an open redirect with a client path traversal.
Attackers can use this to reroute users to a page that has a frontend plugin installed, which will run arbitrary JavaScript. The XSS will function if anonymous access is enabled, and this vulnerability does not require editing permissions,” it continued.
“A full read SSRF can be accomplished by taking advantage of the open redirect if the Grafana Image Renderer plugin is installed.”
According to Ox Security, a malicious link given to the victim is the first in a series of exploits that compromise the vulnerability.
The security vendor went on to say, “When the link is clicked, Grafana uses an external malicious plugin hosted on the attacker’s server.”
The researchers claim that the malicious URLs have the potential to cause the user’s browser to run arbitrary JavaScript.
The exploit can work even with anonymous access enabled and doesn’t require escalated privileges.
The vulnerability enables attackers to alter account credentials, take over user sessions, and read internal resources by using server-side request forgery (SSRF) when the Grafana Image Renderer plugin is installed.
Grafana’s default Content Security Policy (CSP) offers some defense, but because client-side enforcement is limited, it cannot stop exploitation.
Through JavaScript routing logic built into Grafana, OX Security’s hack shows that CVE-2025-4123 may be abused client-side and used to go around contemporary browser normalization protections.
This makes account hijacking through password resets simple by enabling attackers to take advantage of URL handling irregularities to load malicious plugins that alter user email addresses.
The large number of exposed instances and the lack of authentication requirements create a significant attack surface, even though CVE-2025-4123 has several exploitation requirements, such as user interaction, an active user session when the victim clicks the link, and having the plugin feature enabled (which is enabled by default).
Grafana administrators are advised to update to versions listed below; 10.4.18+security-01, 11.2.9+security-01, 11.3.6+security-01, 11.4.4+security-01, 11.5.4+security-01, 11.6.1+security-01, and 12.0.0+security-01 in order to reduce the risk of exploitation.
“Any code can be executed by this malicious plugin on the user’s behalf. In this instance, the code that runs causes the victim’s Grafana username and login email to be changed to values that the attacker controls or may reroute to internal services. The attacker can reset the victim’s password and access their Grafana account by using the altered email.
The firm cautioned that hackers could obtain valuable operational data and business intelligence from a vulnerable organization by breaching a Grafana account. If IT teams lose access to vital systems, they may also cause serious operational problems by excluding authorized users, it continued.
According to Ox Security, “the vulnerability affects Grafana instances running locally by crafting a payload that takes advantage of the locally used domain name and port for the local service,” even though it affects a significant portion of Grafana servers that are publicly accessible.
Related Reading
More contextual TechBooky stories selected from tags, categories and article context.
We use cookies to ensure that we give you the best experience on our website. If you continue to use this site we will assume that you are happy with it.