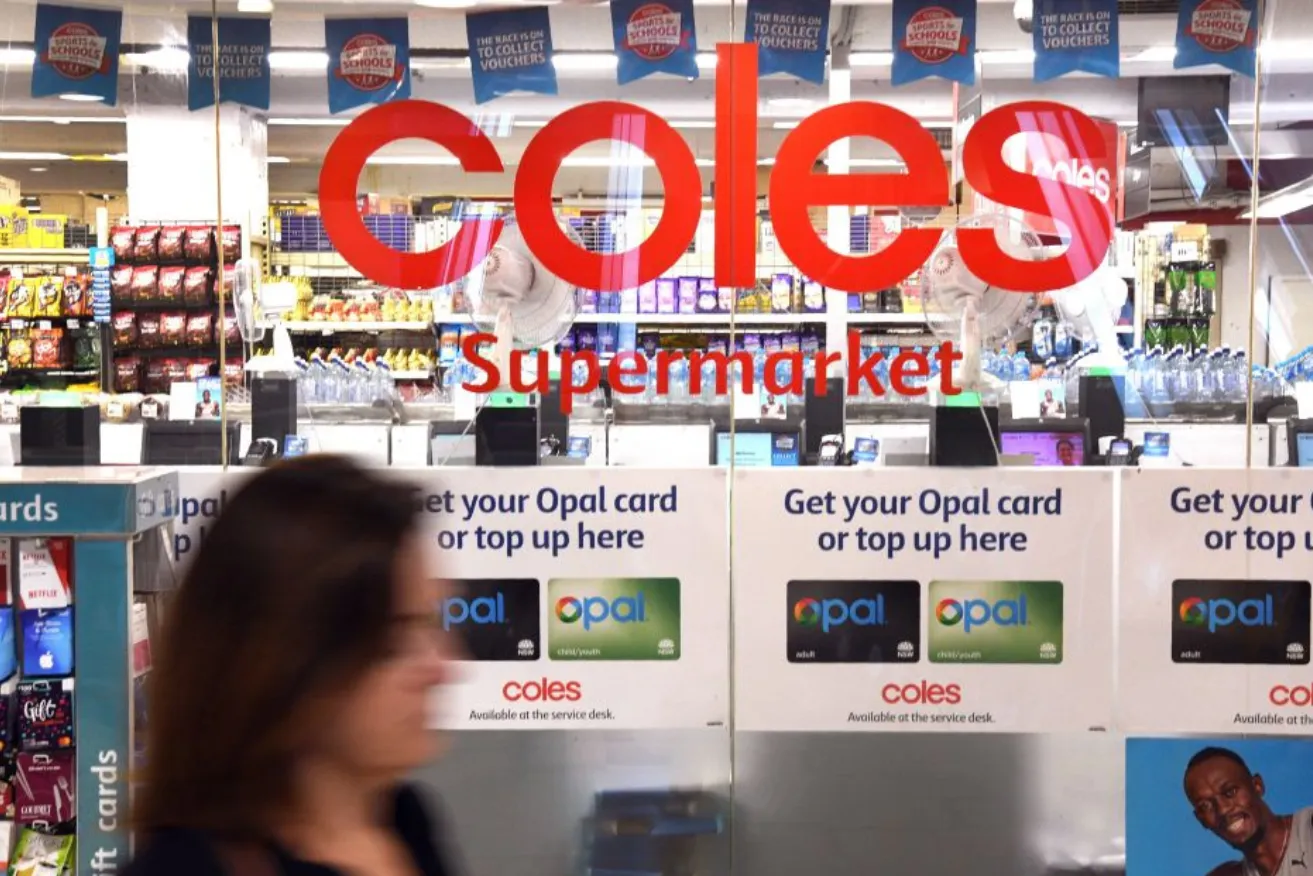
Australian supermarket group Coles is investigating a cyber security incident but says customers can continue shopping in its stores and online. In a market disclosure on 16 November, the company said it had not identified evidence that customer, employee or supplier data had been compromised or removed. That is an important qualification while the investigation continues, rather than a final finding that no information was exposed.
The statement filed with the Australian Securities Exchange gives few technical details. Coles has not disclosed when the activity began, how an intruder may have entered its systems, which systems were affected or who was responsible. It says it is working with the Australian Cyber Security Centre, other relevant authorities and outside security specialists to contain the incident and secure its IT environment.
For shoppers, the clearest operational update is that trading has continued. Coles says stores and online services remain available. The company has not reported a shutdown of tills, deliveries or its website. Equally, uninterrupted shopping does not mean every internal system is unaffected. The statement describes an investigation in progress, so the scale and consequences may change as forensic work proceeds.
Coles also says its investigation has found no evidence so far that customer, team-member or supplier information was taken. It would be misleading to call this a confirmed customer-data breach on the available facts. Companies often need time to establish whether access to a system also led to access to records, and Coles has promised further updates when appropriate.
A supermarket’s digital systems support far more than online orders. Payments, inventory, warehouse operations, staff scheduling and supplier coordination all depend on connected technology. An incident can therefore create business disruption even without a confirmed theft of personal information. At this stage, Coles has not reported such disruption, and there is no basis to assign a financial cost.
Recent retailer incidents show why investigators have to separate one case from another. TechBooky reported that Ahold Delhaize estimated a sales impact from its own cyberattack, while separate European refrigeration disruptions affected chilled goods. Neither story establishes a link to Coles. Similar timing or the fact that all involve retailers is not evidence of a shared attacker, supplier or method.
The next useful disclosure will be whether Coles can identify the systems involved, confirm the extent of any unauthorised access and explain whether trading or data has been affected. For now, the verified story is narrower but still significant: a major Australian retailer has publicly acknowledged a cyber incident, involved national authorities and kept its customer-facing operations running while it investigates.
Related Reading
More contextual TechBooky stories selected from tags, categories and article context.
Paul Femi Balo is the founder and publisher of TechBooky. He covers artificial intelligence, African technology, digital infrastructure, enterprise technology and the global digital economy.
We use cookies to ensure that we give you the best experience on our website. If you continue to use this site we will assume that you are happy with it.