TechBooky AI Assistant
👋 Welcome to TechBooky AI Assistant

I can help with:
🔎 Tech News
🤖 AI Topics
💻 Gadgets
☁️ Cloud
✍️ Guest Posts
📢 Advertising
🔗 Backlinks
📩 Newsletter
  • AI Search
  • Cryptocurrency
  • Earnings
  • Enterprise
  • About TechBooky
  • Submit Article
  • Advertise With TechBooky
  • Contact Us
  • Data Intelligence
TechBooky
  • African
  • AI
  • Metaverse
  • Gadgets
  • Data Intelligence
  • AI Search
Generic selectors
Exact matches only
Search in title
Search in content
Post Type Selectors
Search in posts
Search in pages
  • African
  • AI
  • Metaverse
  • Gadgets
  • Data Intelligence
  • AI Search
Generic selectors
Exact matches only
Search in title
Search in content
Post Type Selectors
Search in posts
Search in pages
TechBooky
Generic selectors
Exact matches only
Search in title
Search in content
Post Type Selectors
Search in posts
Search in pages
Home Open source

NoisyTCP Linux Flaw Could Crash Exposed Servers Remotely

Paul Femi Balo by Paul Femi Balo
November 16, 2026
in Open source, Security
Share on FacebookShare on Twitter
Share this story

Send it to someone who should read it.

f Facebook X X in LinkedIn wa WhatsApp tg Telegram @ Email

In Brief
  • A newly disclosed Linux kernel flaw could let an unauthenticated attacker crash a vulnerable server over the network.
  • Security researcher Hyunwoo Kim calls the bug NoisyTCP and tracks it as CVE-2026-99288.
  • The issue sits in the kernel’s TCP handling, so an ordinary exposed service can provide a route to the fault before a user logs in.

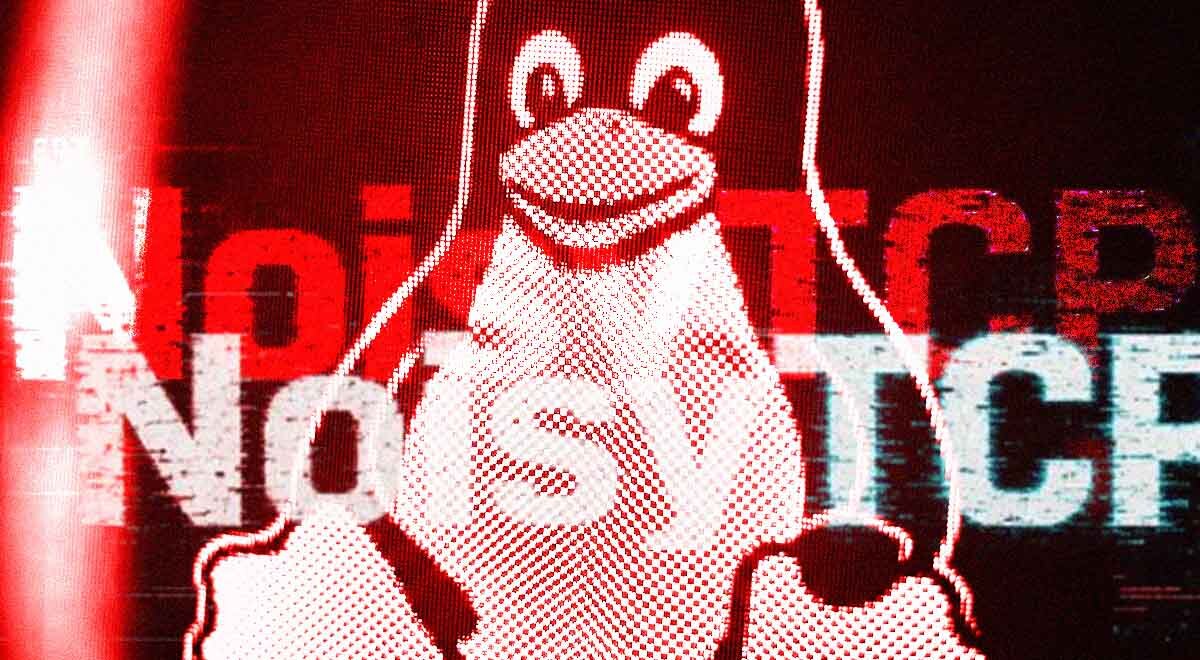
A newly disclosed Linux kernel flaw could let an unauthenticated attacker crash a vulnerable server over the network. Security researcher Hyunwoo Kim calls the bug NoisyTCP and tracks it as CVE-2026-99288. The issue sits in the kernel’s TCP handling, so an ordinary exposed service can provide a route to the fault before a user logs in.

Kim said default configurations of Nginx, Apache and SSH were affected in his tests. The headline risk demonstrated publicly is a kernel panic and denial of service, not confirmed remote code execution. His advisory also describes a harder-to-trigger use-after-free path, but it does not establish a general-purpose exploit for taking control of servers.

How NoisyTCP works

The vulnerability is a race in the Linux TCP stack. Processing of crafted incoming traffic can be split between different receive contexts, leaving a stale socket reference at precisely the wrong moment. Kim said the condition requires at least two receive queues or software that distributes packet processing across multiple CPUs. That makes the risk dependent on a server’s kernel and networking setup, even though the underlying code has been widespread.

In his virtual-machine tests, triggering the crash against common services took about five seconds to two minutes. A quiet physical server took far longer in a tuned test. Those timings show both why the bug matters for internet-facing infrastructure and why it would be misleading to suggest every Linux machine will fail immediately on contact.

Also worth reading
Notion Warns of API Keys in Chats Exposed by Fireworks Breach Critical Apache HTTP/2 Flaw Raises Remote Code Execution Risk Coles Investigates Cyber Incident as Australian Stores Stay Open Palo Alto Networks Earnings Will Test the AI Security Boom Opinion: This Week Will Show Whether the AI Boom Can Pass a Reality Check Amazon Finds AI Agents Stealing Keys to Fund Cyberattacks

Kim traces the vulnerable code to an October 2015 change and identifies the upstream fix as commit 4e2b3ef19e0e, merged on 3 November 2026. Linux distributions package their own kernels and backport fixes, so administrators should consult their vendor’s advisory rather than rely on a broad version number alone. They also need to confirm the patched kernel is the one actually running after an update and restart.

The flaw is particularly relevant to hosts exposing TCP services, including web and remote-access servers. A container does not automatically contain a kernel crash, because containers on the same host share the kernel. Organisations should prioritise exposed systems and assess whether their networking configuration meets the conditions described in the research.

Patch first, then consider mitigations

Applying a vendor-provided kernel fix is the preferred response. Kim describes temporary measures for systems that cannot be patched immediately, including reducing an external interface to one receive queue or disabling SYN cookies. Those changes carry operational and security trade-offs. In particular, disabling SYN cookies weakens a defence against SYN-flood attacks, so it should not be treated as a casual one-line fix.

The disclosure follows a run of high-profile software security findings, but NoisyTCP is a distinct kernel issue. Its practical lesson is familiar: internet-facing infrastructure needs prompt patching, a clear inventory of running kernels and careful testing of any emergency mitigation.

Related Reading

More contextual TechBooky stories selected from tags, categories and article context.

  • 1778005468205
    Critical Apache HTTP/2 Flaw Raises Remote Code…
  • Cohen-Linus-Torvalds
    Linus Torvalds Uses Claude Code On Experimental…
  • 2026-05-08-Linux_LPE-Dirty_Frag-Aufmacher-3f0ce52bb528ed97
    New Linux Zero-Day Flaw 'Dirty Frag' With Root…
  • php1
    PHP Releases Emergency Fixes for Two Critical RCE Flaws
  • MongoDB_Logo
    MongoDB Vulnerability Lets Attackers Crash Servers Remotely
  • 1_3xGQbCBWsXZHmTfkZYGk1Q
    Apple Fixes iMessage Group Chat and Bluetooth Privacy Flaws
  • barracuda
    Barracuda Email Gateway Flaws Could Give Attackers…
  • microsofts-surface-duo-dualscreen-androi-5f1f3d057e8c350ae07dd862-1-jul-28-2020-15-24-20-poster
    Microsoft Patch Tuesday Fixes 63 Bugs, 1 Zero-Day
Keep Reading Smarter

Search TechBooky with AI

Use TechBooky's AI Search to explore the context behind this story and related coverage across the site.

Try AI Search
More On This Topic
Open source Security
Follow TechBooky

Follow TechBooky for more technology stories and newsroom updates.

f Facebook X X in LinkedIn ig Instagram wa WhatsApp

Tags: CVE-2026-99288cybersecurityLinuxNoisyTCP
Paul Femi Balo

Paul Femi Balo

Paul Femi Balo is the founder and publisher of TechBooky. He covers artificial intelligence, African technology, digital infrastructure, enterprise technology and the global digital economy.

Search TechBooky
Open TechBooky AI Search Try the AI Assistant

BROWSE BY CATEGORIES

Receive top tech news directly in your inbox

subscription from
Loading

Freshly Squeezed

  • NoisyTCP Linux Flaw Could Crash Exposed Servers Remotely November 16, 2026
  • Fed Warns AI Agents Could Trigger Bank Runs in Minutes November 16, 2026
  • Coles Investigates Cyber Incident as Australian Stores Stay Open November 16, 2026
  • Apple Tests AI Health Answers in 200,000-Person OpenEvidence Study November 16, 2026
  • SK Hynix Plans $1.05B Push for South Korean Chip Suppliers November 16, 2026
  • Amazon Loses 40 Leo Satellites After ULA Vulcan Launch Failure November 16, 2026
  • Samsung SDS in Early AI Data Centre Talks With OpenAI and Anthropic, FT Says November 16, 2026
  • Jensen Huang Discussed Nvidia CEO Comeback as Allies Lobby Board, FT Reports November 15, 2026
  • Nvidia Faces First Earnings Test Since Jensen Huang’s Exit November 15, 2026
  • Microsoft Ignite 2026 Faces a Test of AI Agents at Work November 15, 2026
  • Petition to Reinstate Jensen Huang as Nvidia CEO Tops 100,000 November 15, 2026
  • Palo Alto Networks Earnings Will Test the AI Security Boom November 15, 2026

Browse Archives

November 2026
M T W T F S S
 1
2345678
9101112131415
16171819202122
23242526272829
30  
« Oct    

Quick Links

  • About TechBooky
  • Advertise With TechBooky
  • Contact us
  • Submit Article
  • Privacy Policy
Generic selectors
Exact matches only
Search in title
Search in content
Post Type Selectors
Search in posts
Search in pages
  • AI
  • Data Intelligence
  • AI Search
  • African
  • Gadgets

© 2025 Designed By TechBooky Elite

Discover more from TechBooky

Subscribe now to keep reading and get access to the full archive.

Continue reading

We use cookies to ensure that we give you the best experience on our website. If you continue to use this site we will assume that you are happy with it.