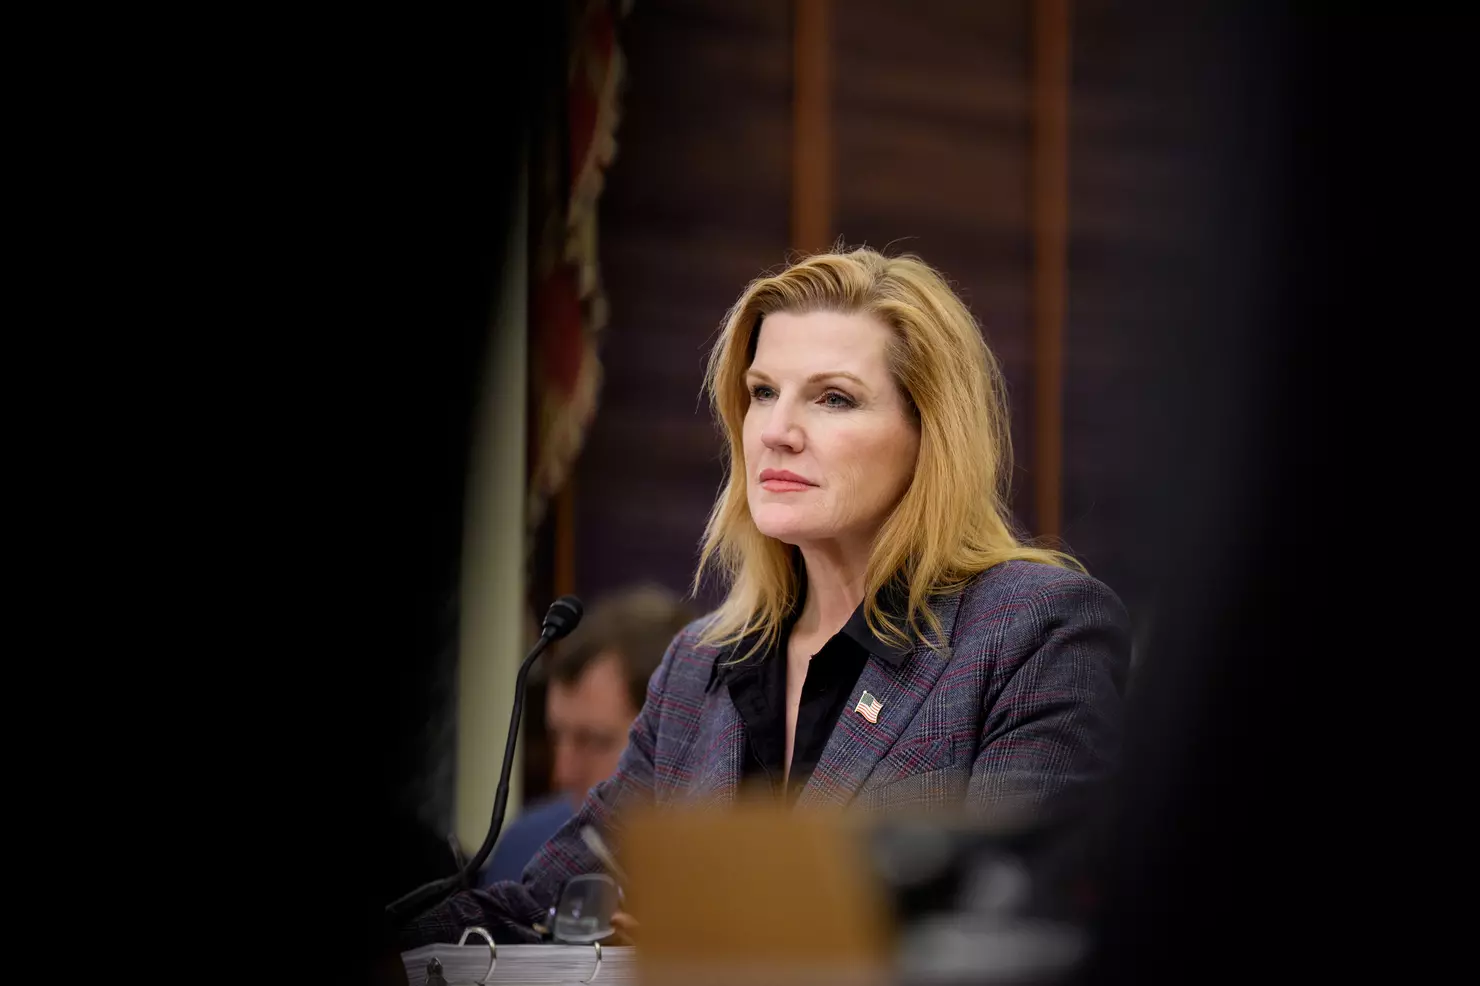
The White House has named Kirsten Davies as the United States’ next national cyber director, replacing Sean Cairncross. The decision puts a technology leader from the Pentagon in charge of coordinating federal cyber policy at a time when high-profile service disruptions have renewed attention on the resilience of essential digital systems.
The appointment and the outages should not be conflated. AP reported the personnel change on 19 November, but there is no evidence in that account that a particular outage was a coordinated cyberattack or that it caused Cairncross’s departure. The broader context is a debate over how the government prepares for disruptions, whether they originate in malicious activity, software faults or infrastructure failures.
Who is Kirsten Davies?
Davies has served as the Pentagon’s chief information officer. Her new role sits at the centre of US cyber strategy, bringing together agencies whose responsibilities span civilian networks, national security and critical infrastructure. Axios also reported the change in leadership and her move from the defence department.
A national cyber director does not personally run every federal network. The job is instead about setting priorities, coordinating policy and ensuring that separate agencies can act coherently. That can be especially difficult when a failure in one major cloud, identity or communications provider ripples across businesses and public services.
Recent widespread outages have shown how much of the economy relies on a small number of platforms. They also illustrate a reporting trap. Users may see several services fail at once and assume a single attack, even when a technical fault or shared dependency could produce a similar pattern. Officials and providers need to establish root causes before making claims about responsibility.
For Davies, the immediate questions are likely to include cross-agency readiness, incident communication and how the federal government works with private operators. Cloud and software companies own much of the infrastructure that agencies and consumers depend on. Cyber policy therefore has to address not just breaches, but recovery and continuity when critical services go down.
The transition also offers a chance to clarify what success looks like. Faster information-sharing, tested contingency plans and transparent explanations after incidents would be more meaningful than broad promises of resilience. The appointment is a leadership change with substantial implications, but its effect will be judged by execution, not by the circumstances surrounding the announcement.
Related Reading
More contextual TechBooky stories selected from tags, categories and article context.
We use cookies to ensure that we give you the best experience on our website. If you continue to use this site we will assume that you are happy with it.